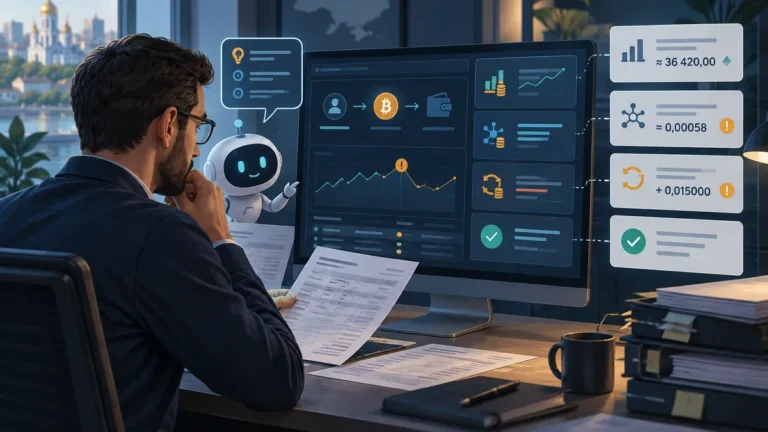
Сигнал ШІ — привід звірити платіж із першоджерелами, а не автоматичний доказ шахрайства.
An online store receives a stablecoin payment, but the amount in its financial report is lower than expected. AI flags the transaction as unusual. That is a reason to check the calculation, not a finding of fraud: the difference could reflect an exchange rate, a payment provider’s fee, a partial refund, or an import error.
A useful process starts with reconstructing the movement of funds, not blocking a payment. The finance team needs to establish what deviated from expectations, which source records support that finding, and who makes the final decision. The following workflow is for businesses accepting crypto payments that want to use AI without placing excessive trust in its answers.
What financial AI can suggest about a payment—and what an alert cannot prove
Financial AI can help compare prepared records, identify unusual relationships, and formulate questions about the data. For example, at https://www.numevia.io/, NUMEVIA advertises analysis of transactions, expenses, and income, alongside chat-based financial analytics. This illustrates how a financial assistant is positioned; it does not establish support for crypto wallets, blockchain monitoring, or a ready-to-use fraud detection system. The service’s terms describe the current build as a front-end demo and state that outputs are not financial advice.
Distinguish a numerical alert from a written explanation. A rule might detect that net proceeds are 3% below expectations. A language model can suggest reasons, but without the provider’s fee schedule, the exchange-rate source, and any refund record, it cannot establish which explanation is correct. Persuasive wording cannot replace a missing document.
An anomaly is a deviation from a chosen baseline, not proof of wrongdoing. A large payment may be normal for a wholesale order, while a series of small payments may fit a subscription business. Compare similar transactions: the same network, provider, and fee calculation method. Otherwise, the system may mix different business scenarios and generate unnecessary alerts.
Exchange rate, fee, or error: which discrepancies to check first
First, identify the amounts being compared: the order price, the number of tokens received, their value in the reporting currency, or net proceeds after deductions. These are different measures. Also record the valuation time: invoice creation, transfer confirmation, and provider conversion may occur at different times. Each step needs the relevant exchange rate and time zone.
Do not automatically treat a stablecoin as exactly one unit of fiat currency in every calculation. The study Will the real stablecoin please stand up? — BIS Papers No 141 examines stablecoin stability and deviations from their pegs, including intraday deviations. The practical implication for reconciliation is to check an unusual reporting-currency amount against the relevant market rate. A price deviation alone does not prove fraud; this is not a BIS recommendation to block payments.
Consider a hypothetical store expecting €1,000 but receiving €990. If the contract specifies a 1% provider fee on that amount and there are no other adjustments, the arithmetic explains the difference. However, do not automatically add a network fee to the store’s costs: the sender may have paid it separately. Verification requires the actual allocation of costs, not a typical scenario suggested by a model.
- Exchange rate: verify the trading pair, quotation source, and time associated with the price.
- Fees: separate the network charge, provider fee, and conversion costs.
- Refunds: check partial refunds, their currency, and their connection to the order.
- Imports: look for duplicates, incorrect decimal places, time shifts, and missing records.
- Status: do not treat a newly created payment or an unconfirmed transfer as a completed settlement.
Check the asset’s identity separately: an identical token symbol does not guarantee an identical contract or network. Reconciliation requires the network, contract address, and transaction identifier. If those fields are missing, the model should identify the gap rather than invent the details.
How to build a review record and test the AI’s explanation
Instead of forwarding the entire ledger, create a record for the specific case. Include the internal order number, timestamp and time zone, network and asset, expected and actual amounts, exchange-rate source, fees, payment status, and related refunds. Keep source documents in your internal system; provide the model only with the necessary fields that you are authorized to share.
The record should also specify the rule that triggered the alert. “The amount is unusual” is insufficient. A better description is: “Net proceeds are €10 below the invoice amount; our rule allows a €2 difference.” This is an illustrative internal threshold, not a universal standard. Set thresholds according to margins, typical fees, and the cost of manual review.
Limit the AI prompt to a verifiable task: “Suggest possible reasons for the difference. For each reason, identify the evidence needed, show the calculation, and state which data is missing. Do not classify the transaction as fraudulent.” This format does not guarantee accuracy, but it makes checking easier. An answer such as “possibly a fee” must lead to a specific comparison between the applicable tariff and the actual deduction.
Repeat the arithmetic in a spreadsheet or accounting system. Verify the status with the provider and, where necessary, check transfer details in the relevant network’s blockchain explorer. Mark each hypothesis as confirmed, rejected, or lacking sufficient evidence. Do not treat the model’s own confidence score as a probability of fraud: without separate validation, it does not have that meaning.
What data to share and how to assess a provider’s claims
Even a public wallet address can become sensitive when combined with a customer’s name, an order, and internal sales history. Use synthetic records or a de-identified sample for initial testing. Replace customer identifiers with random codes, remove contact details, and retain only the fields needed to test the hypothesis. Private keys, seed phrases, and API secrets must never enter the chat.
A provider’s self-description helps frame questions, but it does not complete a security assessment. At https://www.numevia.io/about, NUMEVIA states that it uses modern encryption and secure infrastructure and gives users access to information about AI usage, resource consumption, and analytical results. These statements are not independent security verification and do not, by themselves, explain retention periods or the conditions for processing payment data.
Before sharing real records, obtain documented answers: where is data stored, who can access it, which subprocessors handle it, are prompts used for model training, and how does deletion work? Clarify what happens to backups, how incidents are reported, and whether activity logs are available. If answers are incomplete, restrict the pilot to data that does not reveal customers or commercial details.
The risks of confidently expressed false answers, exposure of sensitive information, and excessive reliance on automation are addressed in Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile — NIST AI 600-1. For a payment team, these risks support checking conclusions against source records and keeping a person responsible for the decision. The document does not establish specific rules for blocking crypto payments.
When to close an alert and when to escalate for manual investigation
Close an alert when documents and calculations confirm its cause—for example, when the difference exactly matches an agreed fee or a linked refund. Save the explanation, sources, and reviewer’s name. If an incorrect import triggered the alert, correct the data processing and check other records affected by the same error. Otherwise, the team will repeat the same investigation unnecessarily.
Escalate a case to the responsible specialist when an explanation contradicts source records, settlement confirmation is missing, the network or asset does not match, or an unexplained refund pattern recurs. Include the facts, not just the AI’s conclusion. Payout restrictions or other actions should follow approved procedures, contractual terms, and applicable requirements—not the persuasiveness of the model’s wording.
For a pilot, assign an owner, a review deadline, and an escalation route. Measure the proportion of confirmed problems, the number of false alerts, and review time; track cases with insufficient data separately. AI’s usefulness lies not in how many payments it flags, but in whether the team reaches reproducible conclusions faster without unnecessary delays for legitimate customers.